Troubleshooting
Microsoft's Internet Information Services (IIS) 10.0 powers millions of websites, but unpatched vulnerabilities can expose systems to severe attacks. These 10 critical security flaws—ranging from remote code execution to denial-of-service risks—demand immediate attention from IT administrators and developers.
CVE-2023-24947: HTTP/2 Request Smuggling Exploit
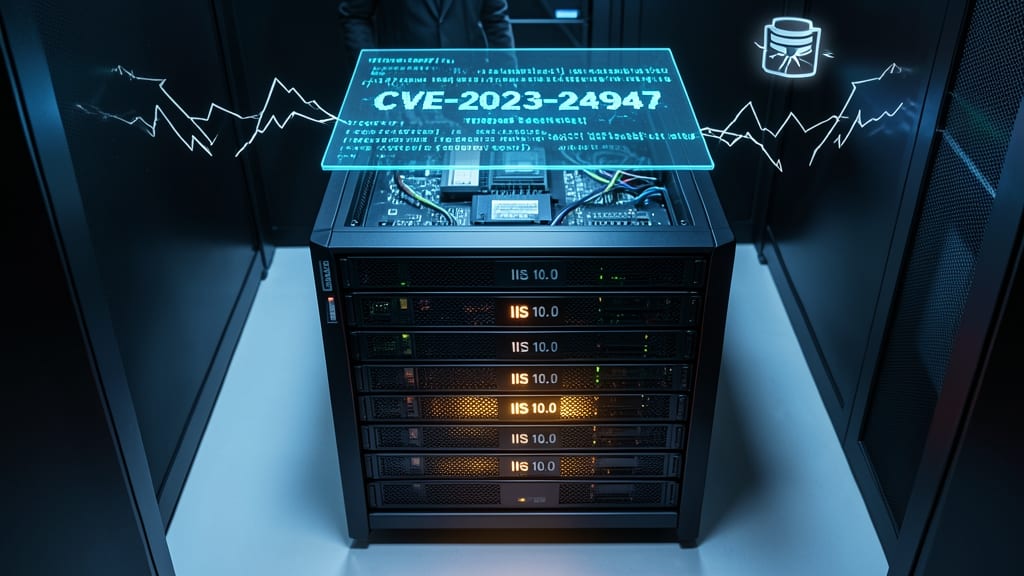
If your IIS 10.0 server runs HTTP/2, you’re at risk of CVE-2023-24947, a critical exploit that lets attackers bypass security controls entirely. This HTTP/2 request smuggling flaw allows malicious actors to manipulate protocol headers, slipping past firewalls and executing arbitrary code on vulnerable systems.
The exploit works by exploiting how IIS 10.0 processes conflicting Content-Length and Transfer-Encoding headers in HTTP/2 requests. Attackers can craft requests that appear valid to the server but trigger unintended behavior—like bypassing Web Application Firewalls (WAFs) or hijacking sessions. Microsoft’s patch for this flaw is urgent, as it affects all IIS 10.0 servers with HTTP/2 enabled by default.
This vulnerability is a silent threat—it doesn’t trigger alerts like brute-force attacks, making it ideal for stealthy compromises. IT admins managing public-facing IIS servers should prioritize patching or disabling HTTP/2 if not absolutely necessary. 💻
CVE-2022-37969: Server-Side Request Forgery (SSRF)
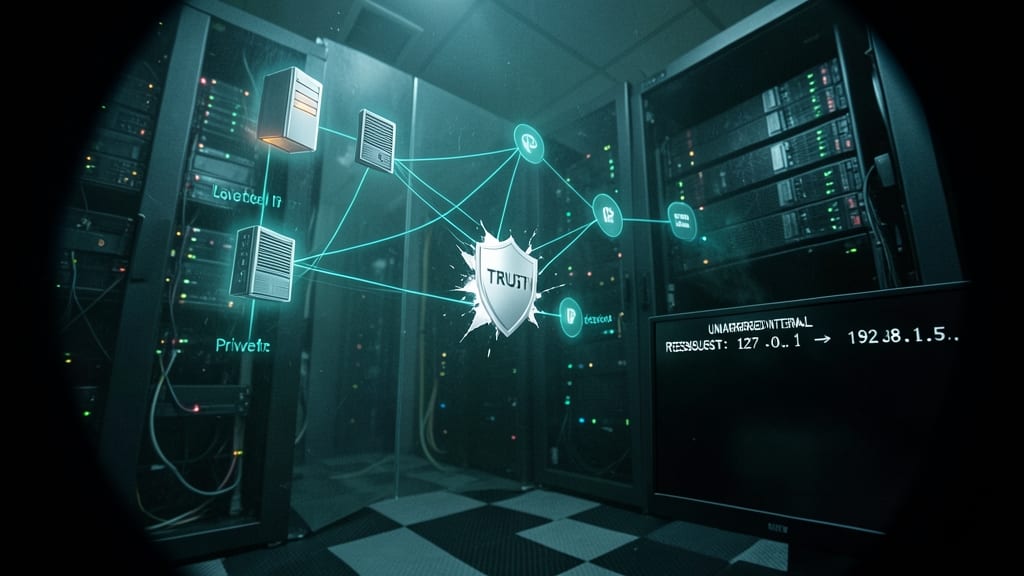
While HTTP/2 exploits like CVE-2023-24947 make headlines, CVE-2022-37969 (SSRF) operates in the shadows—tricking servers into making unauthorized internal requests. Unlike external attacks, this vulnerability doesn’t need direct access; it hijacks the server’s own trust in localhost or private IPs, exposing databases, APIs, or even cloud metadata services.
The flaw stems from improper validation of URL redirection targets in IIS 10.0, allowing attackers to craft requests like http://169.254.169.254 (AWS metadata endpoint) or http://localhost:8080/admin. Microsoft’s patch for KB5014754 (released October 2022) fixes the core issue, but misconfigured firewalls or legacy apps with hardcoded internal URLs remain at risk.
DevOps teams managing hybrid cloud or microservices architectures should prioritize this—especially if your IIS servers interact with internal APIs or container orchestration tools. A single overlooked SSRF can turn a seemingly secure system into a backdoor. 💻
CVE-2021-38666: Memory Corruption in URL Parsing
Imagine a single maliciously crafted URL bringing down your entire IIS 10.0 server—no remote code execution, just pure, unstoppable denial-of-service (DoS). That’s exactly what CVE-2021-38666 delivers, exploiting a memory corruption flaw in URL parsing that crashes the server process instantly.
The vulnerability stems from improper handling of Unicode normalization in URLs, allowing attackers to trigger a heap-based buffer overflow with a carefully constructed request. Microsoft’s patch (via KB5005443) fixes the core parsing logic, but the flaw highlights how even seemingly benign inputs—like URLs—can become attack vectors when not properly validated.
This is especially critical for high-traffic websites or shared hosting environments, where a single malicious request could take down multiple applications. Admins should prioritize patching and consider URL sanitization layers as an extra defense. ⚡
CVE-2020-16875: Authentication Bypass via WebDAV
Shared hosting environments often rely on default IIS 10.0 WebDAV configurations, leaving them vulnerable to CVE-2020-16875—a sneaky flaw that bypasses authentication entirely. Unlike other exploits targeting IIS, this one doesn’t require complex payloads; it simply exploits misconfigured permissions to grant attackers full read/write access to restricted directories.
The vulnerability stems from improperly secured WebDAV endpoints (typically http://server/dav/wwwroot/), where attackers can authenticate as any user by sending a crafted PROPFIND request. Microsoft’s patch for this flaw—part of the November 2020 security update—fixes the core permission-checking logic, but many admins overlook WebDAV entirely unless explicitly enabled.
This exploit is particularly dangerous for shared hosting providers or legacy systems where WebDAV is left enabled for legacy applications. Disabling WebDAV entirely (unless absolutely required) is the simplest mitigation—Microsoft’s own documentation recommends this for environments with mixed trust levels. 💻
CVE-2019-1181: ASP.NET Core Deserialization Flaw
If your ASP.NET Core application relies on default serialization settings, you’re at risk from CVE-2019-1181, a flaw that lets attackers execute arbitrary code by sending maliciously crafted serialized payloads. Unlike other IIS exploits targeting protocols or misconfigurations, this vulnerability exploits trusted deserialization—a common pitfall in modern web apps.
The issue stems from how IIS processes untrusted data during deserialization, particularly when using libraries like Newtonsoft.Json or System.Text.Json. Attackers can craft payloads that bypass authentication and execute commands with the server’s privileges. Microsoft’s patch for .NET Core 2.1 and later includes safeguards, but legacy systems remain exposed unless explicitly updated.
Developers using ASP.NET Core with default settings should prioritize this fix, especially if handling user-uploaded data. The fix requires minimal effort—updating NuGet packages and validating all serialized inputs. 💻
CVE-2018-8626: HTTP Header Injection Attack
What if an attacker could rewrite your website’s response headers to hijack user sessions or inject malicious scripts? CVE-2018-8626 exposes exactly this risk in IIS 10.0, where improper input validation lets attackers inject arbitrary headers—including Set-Cookie or Location—into HTTP responses.
This flaw enables session hijacking (stealing cookies) or XSS attacks by tricking browsers into executing malicious scripts. Microsoft’s October 2018 Patch Tuesday addressed it, but servers still running unpatched IIS 10.0 (especially with custom modules) remain exposed. The attack works by sending crafted requests that bypass header sanitization, making it a silent threat in shared hosting or legacy deployments.
System administrators managing IIS 10.0 should prioritize this patch, especially if using third-party modules or hosting multi-tenant applications where header manipulation could escalate attacks. 💻
CVE-2017-7269: Directory Traversal in IIS Modules
If your IIS 10.0 server relies on custom modules or third-party extensions, you’re at risk of a sneaky attack that bypasses file restrictions entirely. CVE-2017-7269 exploits poorly sanitized path inputs, letting attackers traverse directories to access sensitive files like configuration files, credentials, or even system binaries—without triggering alerts.
The vulnerability stems from flawed input validation in modules that process user-supplied paths, such as URL rewriters or file handlers. A well-crafted request with ../ sequences can trick the server into revealing restricted directories, often without requiring authentication. Microsoft’s patch for this flaw focuses on stricter path normalization, but many legacy modules still lack updates.
This is a silent threat—ideal for attackers who want to gather intel before launching further exploits. Admins managing shared hosting environments or custom-built IIS setups should audit third-party modules immediately and enforce strict file permissions as a stopgap. 🔧
CVE-2016-3296: Kerberos Authentication Bypass
If your IIS 10.0 server relies on Active Directory, CVE-2016-3296 could let attackers silently bypass Kerberos authentication—one of the most trusted Windows security protocols. This flaw exploits how IIS handles Kerberos tokens, allowing unauthorized access without triggering alarms.
The vulnerability stems from improper validation of Service Principal Names (SPNs) in Kerberos tickets, letting attackers forge tokens that trick the server into granting access. Microsoft’s patch for this issue also includes updates to Windows Server 2016 and Windows 10, but many legacy systems remain exposed due to misconfigured SPN registrations or outdated Group Policy settings.
This exploit is particularly dangerous in enterprise environments where Active Directory integration is critical. If you manage IIS servers tied to AD, prioritize applying the patch and auditing your Kerberos delegation settings to close this gap. 💻
CVE-2015-2523: Buffer Overflow in FTP Service
If your IIS 10.0 server still runs FTP services, you’re at risk of a classic yet dangerous stack-based buffer overflow that crashes the entire service when processing malformed commands. This CVE-2015-2523 flaw has been weaponized in automated attack scripts scanning for outdated systems, making it a persistent threat in legacy environments.
The vulnerability stems from improper bounds checking in the FTP service handler, allowing attackers to trigger a denial-of-service (DoS) by sending oversized or malformed commands. Microsoft’s patch (KB3033889) fixes the issue, but many organizations overlook FTP as a potential attack vector—even though it’s often left enabled by default. The exploit is trivial to automate, making it a favorite for script kiddies and botnets targeting unpatched servers.
System administrators managing legacy IIS deployments or FTP-based workflows should prioritize this patch, especially if FTP remains exposed to the internet. Disabling FTP entirely is the safest long-term fix. ⚡
CVE-2023-21569: Log Forgery in IIS Logging Module
Ever wondered how attackers erase their digital footprints after a breach? CVE-2023-21569 exposes a chilling flaw in IIS 10.0’s logging module, letting threat actors forgery log entries to mask malicious activity. This vulnerability turns server logs—your first line of defense—into a weapon for persistence and evasion.
The exploit targets the IIS Logging Module, allowing attackers to rewrite or delete log records entirely. With no authentication required in default configurations, this flaw enables stealthy post-exploitation maneuvers, like hiding backdoors or covering lateral movement. Microsoft’s patch (via KB5027231) fixes the core issue, but organizations must also audit log integrity tools and enable Windows Event Forwarding for redundancy.
This is a must-patch for enterprises relying on IIS logs for forensics or compliance. Security teams should treat this as a wake-up call to verify log authenticity beyond surface-level checks. 💡